Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026
Anúncios
A significant Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026 has sent shockwaves across the nation, revealing critical vulnerabilities and prompting an immediate, large-scale investigation into the extent of the compromise.
An Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026 has sent ripples of concern through national security circles and the public alike. This unprecedented event highlights the ever-present and evolving threat landscape facing critical government infrastructure, demanding immediate attention and robust, coordinated responses.
Anúncios
The Unfolding Crisis: Initial Discovery and Scope
The discovery of a major cybersecurity breach within federal systems in early 2026 has initiated a crisis of significant proportions. Initial reports indicate that the breach was detected through advanced anomaly detection systems, triggering an immediate lockdown of affected networks and a full-scale investigation by top cybersecurity experts from multiple agencies.
Anúncios
The scope of this incident is still being fully assessed, but early indications suggest a sophisticated, state-sponsored attack targeting sensitive government data. This is not merely a data leak but a deep penetration into core operational systems, raising concerns about national security, intelligence assets, and the integrity of critical public services.
How the Breach Was Detected
The detection process involved a combination of cutting-edge AI-driven threat intelligence and human expertise. Cybersecurity analysts observed unusual patterns of data exfiltration and unauthorized access attempts that bypassed conventional security measures, prompting an immediate escalation.
- Advanced behavioral analytics flagged anomalous user activity.
- Real-time threat intelligence feeds correlated suspicious IP addresses.
- Internal security teams initiated forensic analysis upon initial alerts.
- Cross-agency collaboration expedited the identification of the intrusion vector.
Understanding the initial detection mechanisms is crucial for preventing future attacks. The sophistication of the attack vectors employed suggests a well-resourced and determined adversary, forcing a re-evaluation of current defense strategies across all federal departments. The ongoing investigation aims to pinpoint the exact entry points and the full timeline of the compromise.
Impact Assessment: Data Compromise and National Security Implications
The immediate aftermath of the federal systems cybersecurity breach has focused heavily on assessing the full extent of compromised data and its potential impact on national security. Preliminary analyses suggest that a wide array of sensitive information may have been accessed, ranging from classified documents to personal data of federal employees and citizens.
The implications extend beyond mere data theft. The integrity of operational systems, critical infrastructure control systems, and even military communications could be at risk. This scenario demands a multi-faceted response that addresses both immediate containment and long-term resilience.
Categories of Potentially Compromised Data
While a definitive list is pending, experts are working to categorize the types of data that may have been exposed. This includes, but is not limited to, intelligence briefings, defense strategies, economic policy documents, and personal identifiable information (PII).
- Classified national security documents.
- Sensitive diplomatic communications.
- Proprietary technological blueprints.
- Personal information of government personnel.
The compromise of such data could lead to significant geopolitical shifts, espionage activities, and widespread identity theft. The government is working diligently to notify affected parties and implement protective measures for individuals whose data may have been exposed, emphasizing transparency where national security allows.
Governmental Response: Emergency Protocols and Collaborative Efforts
In response to the Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026, the federal government has activated emergency cybersecurity protocols. This includes the immediate formation of an inter-agency task force comprising experts from the Department of Homeland Security (DHS), the Federal Bureau of Investigation (FBI), the National Security Agency (NSA), and various other intelligence and defense organizations.
The primary objectives of this task force are to contain the breach, eradicate the threat, recover compromised systems, and conduct a thorough forensic investigation to identify the perpetrators. This collaborative approach is critical, as the complexity and scale of the attack necessitate a unified and coordinated effort.
Key Response Actions Undertaken
Several critical steps have been initiated to address the breach. These actions range from isolating affected networks to deploying advanced threat hunting tools across federal infrastructure. The focus is on preventing further compromise and restoring trust in federal digital systems.
- Activation of incident response plans across all federal agencies.
- Isolation of compromised network segments to prevent lateral movement.
- Deployment of advanced forensic tools for detailed analysis.
- Collaboration with private sector cybersecurity firms for specialized expertise.
The government’s rapid response demonstrates the seriousness with which this breach is being treated. Public statements from high-ranking officials have underscored the commitment to national security and the protection of citizen data, while also cautioning against speculation during the ongoing investigation.
The Role of Advanced Persistent Threats (APTs) in Federal Breaches
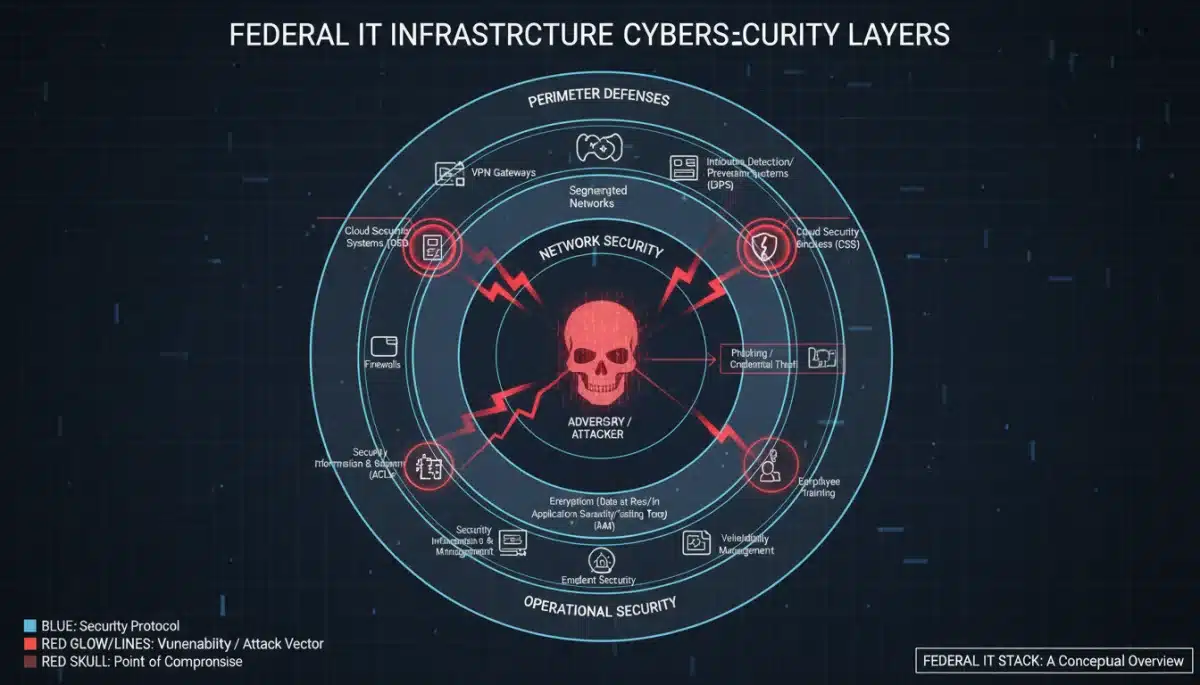
The sophistication of the recent Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026 strongly suggests the involvement of an Advanced Persistent Threat (APT) group. APTs are typically state-sponsored or highly organized criminal entities with significant resources, expertise, and a long-term agenda to infiltrate target networks and exfiltrate data covertly.
Unlike opportunistic cybercriminals, APTs often employ multi-stage attacks, custom malware, zero-day exploits, and social engineering tactics to achieve their objectives. Their patience and ability to remain undetected for extended periods make them particularly dangerous, posing a formidable challenge to even the most robust cybersecurity defenses.
Characteristics of APT Attacks
Understanding the hallmarks of APT attacks is crucial for developing effective countermeasures. These groups often conduct extensive reconnaissance, tailor their attacks to specific targets, and maintain persistence within compromised networks.
- Long-term planning and execution of attacks.
- Use of highly sophisticated and custom-built malware.
- Targeting specific high-value information or critical infrastructure.
- Ability to evade conventional detection methods for extended periods.
The ongoing forensic analysis will likely uncover more details about the specific APT group responsible for this breach. Identifying the adversary’s tactics, techniques, and procedures (TTPs) is paramount for developing more resilient defensive strategies and for potential attribution.
Future of Federal Cybersecurity: Enhancements and Policy Changes
The Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026 serves as a stark reminder of the urgent need for continuous innovation and adaptation in federal cybersecurity. This incident will undoubtedly accelerate the implementation of new security technologies, strengthen existing protocols, and lead to significant policy changes aimed at fortifying national digital defenses.
Expect to see increased investment in artificial intelligence and machine learning for threat detection, greater emphasis on zero-trust architectures, and enhanced international cooperation on cybersecurity intelligence sharing. The goal is to build a more proactive and resilient defense posture that can withstand future sophisticated attacks.
Key Areas for Improvement
Several critical areas are being targeted for immediate and long-term improvement. These include upgrading legacy systems, fostering a culture of cybersecurity awareness, and developing a more agile incident response framework.
- Mandatory adoption of multi-factor authentication across all federal systems.
- Regular, unannounced penetration testing and red team exercises.
- Increased funding for cybersecurity research and development.
- Enhanced training programs for all federal employees on cyber hygiene.
The federal government is committed to learning from this incident and emerging stronger. The breach underscores that cybersecurity is not a one-time fix but an ongoing, dynamic process requiring constant vigilance and evolution.
Public Trust and Transparency in the Wake of the Breach
Maintaining public trust is paramount in the aftermath of a major incident like the Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026. The government faces the delicate balance of providing transparency to its citizens while safeguarding sensitive investigation details and national security interests.
Clear, consistent communication from official sources is crucial to prevent misinformation and undue panic. Citizens need to be assured that their data is being protected and that the government is taking all necessary steps to address the breach and prevent future occurrences. Rebuilding and reinforcing this trust will be a long-term endeavor.
Government Communication Strategies
Effective communication during a crisis involves regular updates, accessible language, and direct engagement with the public. This helps in managing expectations and providing accurate information.
- Regular press briefings by designated spokespersons.
- Establishment of dedicated public information hotlines and websites.
- Collaboration with media outlets to disseminate accurate information.
- Issuance of clear guidelines for citizens on personal data protection.
The government’s approach to transparency and public engagement will be a key factor in how quickly public confidence is restored. Open dialogue, within the bounds of national security, is essential for a resilient and informed populace.
| Key Aspect | Brief Description |
|---|---|
| Discovery Date | Early 2026, detected by advanced anomaly systems. |
| Targeted Systems | Sensitive federal operational and data systems. |
| Primary Threat | Likely sophisticated, state-sponsored APT group. |
| Government Response | Inter-agency task force, emergency protocols, enhanced security. |
Frequently Asked Questions About the Federal Cybersecurity Breach
The breach was a sophisticated intrusion into sensitive federal operational and data systems, uncovered in early 2026. It is suspected to be the work of a state-sponsored Advanced Persistent Threat (APT) group, aiming for long-term data exfiltration and potential disruption.
While specific agencies are not fully disclosed for national security reasons, the breach impacted various critical federal systems. These include networks handling classified information, sensitive diplomatic communications, and potentially personal data of government employees and citizens.
An inter-agency task force has been established, activating emergency cybersecurity protocols. Measures include isolating compromised networks, deploying advanced forensic tools, collaborating with private sector experts, and enhancing real-time threat intelligence sharing to contain and eradicate the threat.
The breach poses significant national security risks due to potential compromise of classified data. It also challenges public trust, necessitating transparent and consistent communication from the government to assure citizens about data protection and ongoing efforts to secure federal digital infrastructure.
The incident is expected to drive substantial enhancements in federal cybersecurity. This includes increased investment in AI/ML for threat detection, wider adoption of zero-trust architectures, mandatory multi-factor authentication, and improved employee training to build a more resilient defense posture.
Conclusion
The Urgent Alert: Major Cybersecurity Breach in Federal Systems Uncovered in Early 2026 represents a critical juncture for national cybersecurity. This incident underscores the persistent and evolving nature of cyber threats, demanding an adaptive and proactive defense strategy. While the immediate focus remains on containment and investigation, the long-term implications will undoubtedly reshape federal cybersecurity policies, technological investments, and inter-agency collaboration. The commitment to strengthening digital defenses and maintaining public trust will be paramount in navigating this complex challenge and emerging with a more resilient and secure national infrastructure.